

What the Century City team needed
The brief came from a legal support team in Century City, Cape Town that was juggling case files, shared client systems and multiple cloud services used by lawyers and support staff. They needed a practical way to stop passwords being passed around in chat threads and spreadsheets, while still keeping access fast enough for a busy office where work shifts between matters all day.
The team also wanted a setup that would suit remote staff and outside consultants without making the admin burden heavier for their internal coordinator. Their priorities were clear: secure password sharing, role based access, proper offboarding and a way to review who had access to what before problems surfaced.
Constraints from a legal environment
Legal support teams handle sensitive information, so the setup had to fit strict internal controls and keep a proper trail of access decisions. There was no room for casual sharing or broad permissions, and the team needed a system that could be explained easily to staff with different levels of technical confidence. Load shedding also mattered because people sometimes worked from home or from satellite offices when power was off, so remote access had to stay simple and reliable.
The team asked for a phased rollout rather than a sudden switch. That meant we had to map the current login habits, identify the most used systems and avoid disrupting daily case work. We also had to account for municipal and client security expectations, especially around staff departures, temporary access and monthly review cycles.
- Shared systems needed to be controlled by role, not by individual memory.
- Access had to be easy to revoke when staff changed projects or left.
- Training needed to be short, practical and suitable for mixed user skill levels.
- The final setup had to support both office based and remote staff.
What we supplied and set up
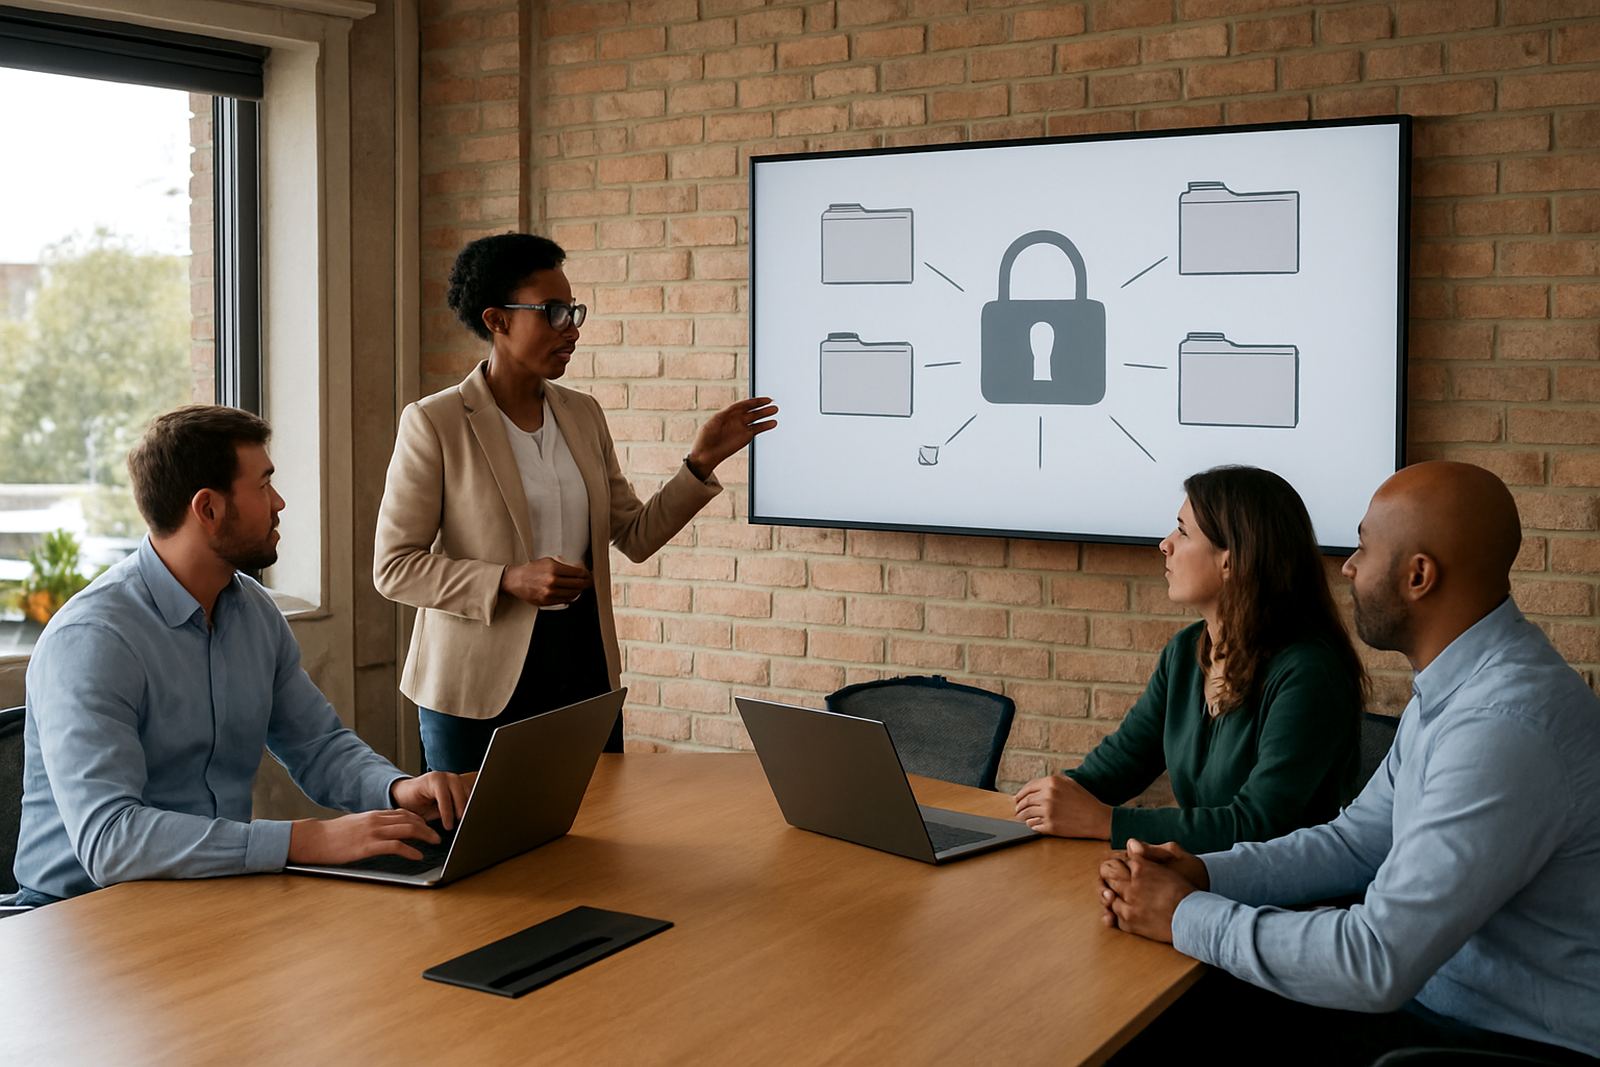
We started with an initial security review and then moved into platform setup, SSO configuration and vault structure design. The vaults were arranged by department and function so sensitive logins could be grouped properly, with clear permission mapping for support staff, supervisors and administrators. That kept the legal team from relying on one shared bucket for everything, which is where mistakes usually creep in.
We also handled password migration from the team’s existing storage methods into the new structure. During this phase we checked for duplicates, weak entries and old accounts that should not have stayed active. A small number of logins were tied to legacy tools and these had to be cleaned up one by one, which took a bit longer than expected but prevented confusion later on.
- Initial Security Review
- Platform Setup
- SSO Configuration
- Vault Structure Design
- Permission Mapping
- Password Migration
- Offboarding Process Design
Training for admins and day-to-day users
Once the core setup was in place, we ran user onboarding training for the full team and admin training for the people who would handle access requests, resets and reviews. The training focused on real tasks, not theory. Staff learned how to store credentials, share access safely, use single sign-on for common tools and flag an issue before it became a security gap.
The admin session covered quarterly access reviews and the offboarding process. That gave the team a repeatable way to check who still needed access, who had changed roles and which shared items should be removed or updated. Revasha from customer success supported the rollout process closely, while Kgosi handled implementation questions and Zaheer assisted with technical support during the first few weeks.
- Clear login habits for everyday work
- How to approve or revoke access without delays
- How to record reviews for internal compliance
- What to do when a staff member leaves or changes matters
Timeline and rollout across the team
The project ran over four weeks. Week one covered the security review and requirements capture. Week two focused on vault design, permission mapping and SSO configuration. Week three was used for password migration and testing, and week four covered training, live rollout support and the first review of access groups.
The rollout was handled remotely with check ins from our Woodstock base, which worked well for a Century City team that needed fast turnaround without losing a whole day to site visits. A few permissions had to be adjusted after staff feedback, especially for shared matter related systems, and those changes were completed quickly. Nothing dramatic, just the kind of fine tuning that makes the setup easier to live with.
Results after the first review cycle
After the first access review cycle, the team had a cleaner view of who could use which systems and why. Password sharing moved out of informal channels and into controlled vaults, which reduced confusion and made it easier to keep sensitive logins in one place. Staff also reported fewer interruptions when people were on leave or working remotely, because the access process was now clearer.
The legal support team now has a stronger routine for onboarding and offboarding, with fewer ad hoc requests and less time spent chasing login details. The setup also gave management a practical record of permission changes, which helps when a matter team grows, shrinks or changes focus. In day to day use, that matters more than fancy features, because the real win is simply not having to hunt for passwords at 4:30 on a Friday.
- Better control over sensitive shared access
- Less reliance on informal password handovers
- Faster onboarding for new staff and contractors
- Cleaner quarterly access reviews
What we would do again
If we were starting the Century City Legal project again, we would follow the same approach: security review first, then vault design, then training and access review routines. That order kept the team from getting overwhelmed and made the rollout easier to absorb. We would also keep the short support window after go live, because the first few weeks are when small permission mistakes are most likely to show up.
For legal and professional services teams, the main lesson is that security works better when it fits the way people already work. A clean structure, sensible permissions and a proper offboarding process are enough to remove a lot of day to day friction. The Century City team now has that in place and can keep building on it as the firm changes.
Key facts
| Client type | Legal support team |
|---|---|
| Location | Century City, Cape Town |
| Rollout length | 4 weeks |
| Core services | Password management and single sign-on |
| Security controls | Role based permissions, offboarding, quarterly access reviews |
| Delivery model | Remote onboarding with national support |