

Why one password is not enough for a small team
Most small businesses rely on a mix of message, accounting tools, project systems, cloud storage and banking platforms. If a password gets copied, guessed or reused somewhere else, that account can be opened from anywhere. For a team in Cape Town, Johannesburg or Durban, that risk does not change just because the office is small.
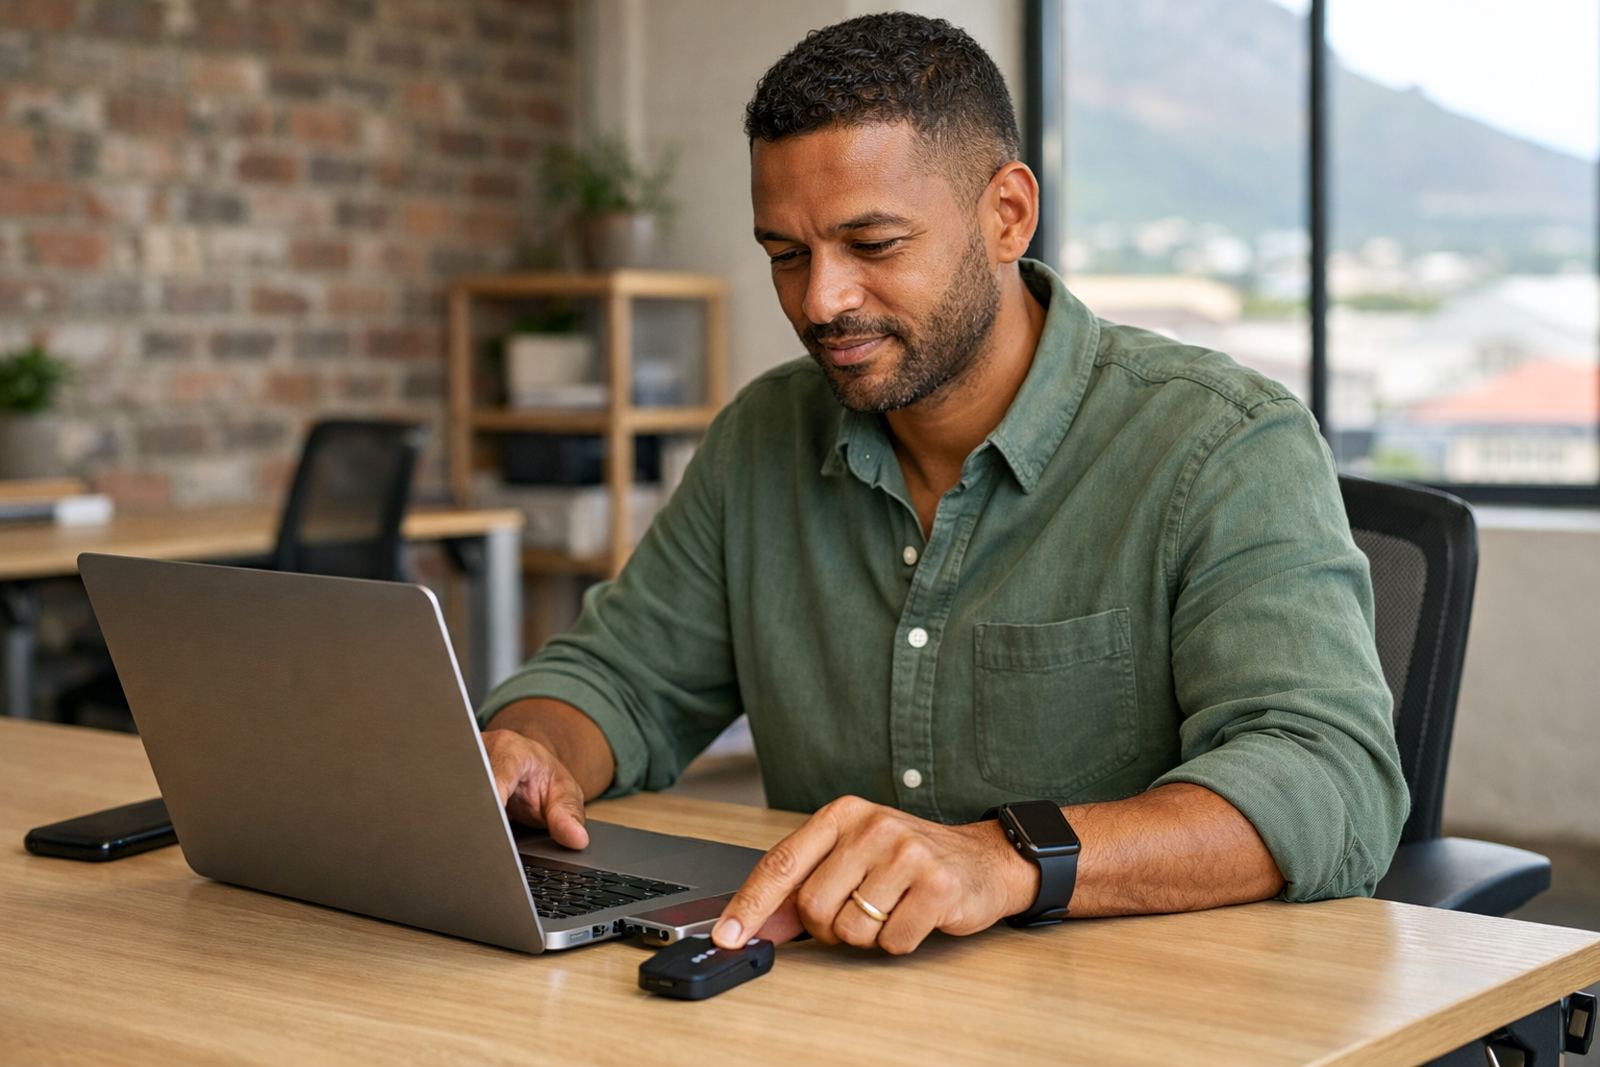
MFA, or multi-factor authentication, asks for something more than a password. That second step might be a code from an app, a hardware token or a prompt on a trusted device. It makes it much harder for someone to get in even if they have the password already. That matters when staff work from the office, from home, from a client site or while travelling between branches.
Many smaller teams think cyber incidents only happen to large companies, but that is not how it works. Smaller businesses often have fewer checks in place and one shared inbox or one recycled password can expose several systems at once. A practical MFA setup gives the whole team a better starting point without making daily work difficult.
Where MFA makes the biggest difference in day to day work
MFA is most useful on accounts that control money, customer data or admin access. That includes message, payroll, file storage, accounting software, banking portals and anything used to reset other passwords. If a person can use one login to reach many systems, that login needs stronger protection.
- Owner and director accounts that can approve changes or payments
- Shared admin accounts used to manage staff access
- Sales and support tools that hold client records
- Cloud storage with contracts, invoices and ID documents
- Remote access accounts used outside the office
In a small office, people often move quickly and share access to keep work going. That is understandable, but it can create gaps. MFA helps close those gaps by making sure access is confirmed by the right person, not just the right password. If someone leaves a laptop behind at a coffee shop in Woodstock or on a train into Pretoria, the extra step can stop a casual login from turning into a security issue.
What smaller teams get wrong about MFA
One common mistake is leaving MFA for later because the business feels too small to matter. Another is switching it on for one app and forgetting the rest. If only one system uses MFA while the main inbox does not, the weak point still remains.
Some teams also worry that MFA will slow staff down. It can, if it is set up badly. But when the method is matched to the role and the workflow, the delay is usually only a few seconds. That is a fair trade for keeping out unauthorised logins, especially when staff are working across suburbs, towns and home offices with patchy connectivity. Load shedding can already interrupt the day, so the login process should not add extra stress.
Another issue is depending on one person to manage all access without a clear process. When someone joins, moves roles or leaves, access should be reviewed straight away. MFA works best when it is part of a wider access plan, not a one-off switch.
A practical setup that works for South African small business
A useful MFA rollout starts with the most sensitive systems first. Message and admin accounts usually come first, then finance tools and shared business platforms. After that, the rest of the team can be brought in by role, rather than all at once.
For a business with staff in Woodstock, Johannesburg, Durban and Gqeberha, the setup should be simple enough for local and remote staff to follow. That means clear instructions, a backup method if a phone is lost and a way to recover access if someone changes device. It also helps to test the process before a busy month-end or payroll run.
- Start with accounts that can reset or control other accounts
- Choose one standard method for most staff
- Keep recovery steps written down and easy to follow
- Review who can approve access changes every quarter
- Remove old devices and old logins when staff leave
A tidy setup also makes support easier. When the process is the same across the team, people spend less time guessing what to do. That matters for a small business where every interruption takes attention away from customers and daily operations.
How MFA fits with password management and SSO
MFA does not replace good password habits. It works best alongside a password manager and single sign-on. A password manager reduces reused passwords and keeps login details stored securely. SSO reduces the number of separate logins staff need to remember. MFA adds the extra checkpoint when someone tries to get in.
Used together, these tools can make access simpler, not harder. Staff are less likely to write passwords on paper or reuse the same one across several systems. Admins can also see who has access to what, which is useful when a team grows from five people to fifteen or more.
For smaller firms, this is not about building a complicated security stack. It is about reducing common mistakes. If one person has to manage all the logins in their head, things get messy quickly. A proper system gives structure without making the team jump through hoops.
What to check before you switch MFA on
Before turning on MFA across the business, check a few basics. Make sure everyone has a current work email address. Confirm that the business knows who owns each account. Decide what happens when a phone is replaced, a device is lost or a staff member is off site with no signal. These are the small things that usually cause delays.
It also helps to have an offboarding process ready. When someone leaves, access should be removed on the same day, not later in the week. MFA is stronger when it is backed by proper account cleanup. If a former employee still has a working login, the extra verification step does not solve that problem.
For teams with staff in different towns or working remotely, training matters too. People need to know how to set up the app, how to use backup options and who to contact if a login stops working. A short training session can prevent a lot of avoidable support calls.